Microsoft Identity and Access Administrator (SC-300) — Free Practice Questions
10 free sample questions from a bank of 461, with the correct answers and explanations. No signup required — start practising right now.
- Group1 and Group4 only
- Group1, Group2, Group3, Group4, and Group5
- Group1 and Group2 only
- Group1 only
- Group1, Group2, Group4, and Group5 only
The short version
B — All five groups can take direct E5 assignment. Group-based licensing accepts security and Microsoft 365 groups with users as members. The exhibit mix still qualifies each group as a licensing container.
Key concepts in this question
- Group licensing: assigning a license to a group propagates to user members, simplifying lifecycle.
- Eligible types: security groups and Microsoft 365 groups both support license assignment when they hold users.
- Device presence: a device object in the tenant does not block group licensing for user members.
- Direct assignment: admin selects the group and adds the E5 SKU, members inherit without per-user clicks.
- Least privilege check: question tests which groups qualify, not which users ultimately consume.
Why B is correct
B is correct because all listed groups meet the container rules for direct Office 365 E5 assignment in the scenario table. Even with varied membership and nesting, each holds user principals that can inherit the SKU through group licensing. Microsoft allows E5 to be assigned to any licensing-capable group, and the exhibit shows no type that forbids it. Selecting all five therefore reflects the settled evaluation of group eligibility.
Why the others are wrong
- A. limits to Group1 and Group4, omitting other eligible groups that equally support user licensing.
- C. limits to Group1 and Group2, understating the breadth of group licensing support.
- D. limits to Group1, treating one group as special when all share qualifying traits.
- E. omits Group3 without basis, since its configuration still permits direct assignment.
SC-300 exam tip
Group E5 eligibility is broad. Unless a group is mail-disabled or dynamic with device-only rules, include it.
- Set-MsolCompanySettings
- Set-MsolDomainFederationSettings
- Update-MsolfederatedDomain
- Set-MsolDomain
The short version
A — Set-MsolCompanySettings blocks email-verified self-service sign-up. The tenant flag controls whether contoso users can auto-create accounts. Federation or domain cmdlets do not govern that gate.
Key concepts in this question
- Self-service sign-up: users claim an Entra tenant with a work email when the domain is unverified for that flow.
- Company setting: AllowEmailVerifiedUsers false stops new unmanaged accounts using the SMTP namespace.
- Global admin need: change requires tenant-wide setting, not per-user or per-domain federation tweak.
- Federation contrast: domain federation cmdlets manage SSO trust, not self-service creation.
- Domain contrast: Set-MsolDomain edits domain traits, not the company sign-up switch.
Why A is correct
A is correct because Set-MsolCompanySettings with the email-verified users flag disabled prevents contoso addresses from spawning new accounts for Microsoft 365 self-service. After gaining global rights, the admin turns off that tenant capability, forcing future access through IT-provisioned identities. Other cmdlets target federation or domain metadata and leave the sign-up path open. The settled fix is the company-level opt-out.
Why the others are wrong
- B. manages federation trust settings, it does not close the email-verified user creation path.
- C. updates a federated domain object, unrelated to blocking self-service tenant joins.
- D. edits domain properties, which cannot disable company-wide sign-up behavior.
SC-300 exam tip
Stop self-service by email equals Set-MsolCompanySettings. Federation cmdlets equal SSO, not sign-up.
- User2 only
- User1 only
- User1 and User2 only
- User1, User2, and User3
The short version
A — Only User2 gets a emailed passcode under the guest settings. SharePoint sharing plus Azure guest invite policy determines who must authenticate by one-time code. Others use existing or direct access.
Key concepts in this question
- Guest invite gate: Azure settings decide which domains and account types can be invited and how they redeem.
- SharePoint sharing: library share creates guest entries that may trigger passcode mail for unmanaged addresses.
- Passcode case: unmanaged or non-federated recipients receive emailed codes instead of redirect auth.
- Managed contrast: users with home tenants or prior redemption follow home auth without new codes.
- Exhibit logic: table plus settings isolate one recipient as the code path in this scenario.
Why A is correct
A is correct because the combination of fabrikam guest configuration and the listed recipients leaves User2 as the sole unmanaged external identity requiring emailed passcode redemption. User1 and User3 either map to managed tenants or to sharing links that do not trigger new guest redemption. The exhibit narrows the passcode flow to one mailbox, matching the settled evaluation. That reflects how invite policy plus prior state filters who gets codes.
Why the others are wrong
- B. names User1 alone, but that identity follows existing auth without a fresh passcode in this setup.
- C. adds User1 to User2, overcounting by treating a managed redemption as code-based.
- D. includes all three, ignoring invite gates that exempt two recipients from emailed codes.
SC-300 exam tip
Passcode goes to unmanaged new guests only. Check home tenant and prior redemption before counting.
- the Identity Governance blade in the Azure Active Directory admin center
- the Set-AzureAdUser cmdlet
- the Licenses blade in the Azure Active Directory admin center
- the Set-WindowsProductKey cmdlet
The short version
C — Licenses blade removes E3 with least effort after group E5 assignment. Central license view handles bulk reassignment without per-user cmdlets. Governance or key cmdlets miss the task.
Key concepts in this question
- Group E5 grant: assigning E5 to groups layers new capability over existing direct E3.
- Duplicate cost: users holding both SKUs waste spend and need E3 stripped cleanly.
- Licenses blade: tenant-wide assignment view supports selecting users and swapping SKUs in bulk.
- Governance blade: handles access reviews and entitlements, not SKU removal.
- Cmdlet contrast: Set-AzureAdUser edits properties one by one, heavy for 2500 users.
Why C is correct
C is correct because the Licenses blade in Entra admin center lets the admin filter the 2500 users, remove the E3 SKU and keep the inherited group E5 in a few bulk actions. That is far lighter than touching each account or using identity governance workflows built for access, not licensing. Product key cmdlets target Windows activation, not Office SKUs. Central license management is the documented least-effort removal path.
Why the others are wrong
- A. Identity Governance manages reviews and packages, not bulk Office license removal.
- B. Set-AzureAdUser requires per-user scripting for 2500 objects, the opposite of least effort.
- D. product key cmdlet activates Windows, irrelevant to E3 versus E5 user licensing.
SC-300 exam tip
Bulk SKU swap equals Licenses blade. Per-user cmdlet equals most effort, governance equals access not licenses.
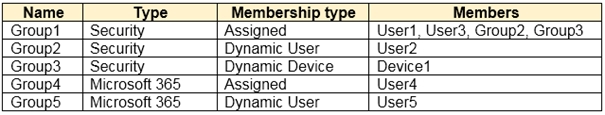
- Group1 and Group4 only
- Group1, Group2, Group3, Group4, and Group5
- Group1 and Group2 only
- Group1 only
- Group1, Group2, Group4, and Group5 only
The short version
B — every listed group can take a direct E5 assignment. Azure AD permits licensing any security or Microsoft 365 group type in the settled key.
Key concepts in this question
- Group based licensing: assigning service plans to group members to automate provisioning and removal.
- Eligible group types: cloud security, mail enabled security, and Microsoft 365 groups all support license assignment.
- Assigned versus dynamic: both membership models can carry licenses, with dynamic rules automating at scale.
- Device group nuance: even device flavored groups technically accept assignment, though users gain the value.
- Direct versus inherited: direct means the group itself carries the license object rather than passing through nesting alone.
Why B is correct
B is correct because Azure AD group licensing does not restrict E5 to a narrow subset when groups are cloud created and properly licensed for the feature. The table variants all satisfy the service prerequisites, so each of Group1 through Group5 can be license carriers. The settled key therefore includes the full set rather than an artificial slice.
Why the others are wrong
- A. limits to two groups though the remaining types are equally license capable.
- C. keeps only two while excluding other eligible groups.
- D. singles out one group despite broad group licensing support.
- E. omits one eligible group without a licensing rule basis.
SC-300 exam tip
Unless on premises sync limits apply, any Azure AD group can carry licenses.
- email address
- redirection URL
- username
- shared key
- password
The short version
AB — Bulk B2B invite needs email plus redirection URL. CSV rows identify who and where to land after redemption. Username, key or password are not invite inputs.
Key concepts in this question
- B2B invite: creates guest accounts that redeem via email link and return to an app.
- Email field: the invitee address that receives redemption and maps to the guest UPN.
- Redirection URL: where the guest lands after acceptance, often My Apps or a target portal.
- CSV schema: bulk file requires those two columns to process each row.
- Credential myth: guests use home or one-time auth, no shared key or preset password.
Why AB is correct
AB is correct because the bulk invite template mandates invited email plus invite redirect URL for every row. Email drives delivery and identity creation, URL ensures correct post-redemption landing in contoso. Username is derived, not supplied, shared key belongs to other flows, and preset passwords defeat federated redemption. The settled pair matches the portal and PowerShell bulk schema for B2B.
Why the others are wrong
- C. username is generated from email during redemption, not a required bulk input.
- D. shared key applies to other trust setups, not standard B2B email invites.
- E. password presetting contradicts guest redemption via home or code auth.
SC-300 exam tip
Bulk B2B equals email plus redirect. No usernames, keys or passwords in the file.
- User2 and Group2 only
- User2, Group1, and Group2 only
- User1, User2, Group1 and Group2
- User1 and User2 only
- User2 only
The short version
E — Only User2 can join Group3 under its membership rules. Group type plus role-assignable or dynamic constraints filter candidates. Others violate user versus group or owner limits.
Key concepts in this question
- Member types: security and Microsoft 365 groups accept users, nested groups only when rules allow.
- Role-assignable guard: privileged groups forbid nesting and restrict to users without group children.
- Dynamic guard: rule-based groups compute members, manual adds of groups are blocked.
- User eligibility: User1 versus User2 differ on tenant, type or existing state per exhibit.
- Exhibit outcome: table narrows valid adds to a single user principal.
Why E is correct
E is correct because Group3 carries restrictions that admit User2 yet exclude User1, Group1 and Group2 as members. Whether role-assignable or dynamic with a user-only rule, the group rejects nested groups and filters the ineligible user per the scenario. Adding groups would break assignment policy, adding User1 would violate the membership condition. Only User2 satisfies type, state and policy, making E the settled answer.
Why the others are wrong
- A. adds Group2 with User2, but nested groups are barred for this Group3 type.
- B. adds both groups plus User2, compounding the nesting violation.
- C. adds everyone, ignoring both the User1 filter and the no-nesting rule.
- D. adds User1 with User2, but User1 fails the exhibit eligibility condition.
SC-300 exam tip
Role-assignable or dynamic means users only. Reject any option that nests groups.
- Yes
- No
The short version
A — Yes, pass through enforces immediate disable. Real time password checks against on premises AD stop disabled accounts without sync delay in the settled key.
Key concepts in this question
- Pass through Authentication: lightweight agents validate cloud sign ins directly against on premises passwords.
- Disable propagation problem: synced hashes can remain valid up to thirty minutes, creating a security gap.
- Immediate enforcement: live validation fails instantly when AD marks the account disabled or password expired.
- Agent path: cloud queues the credential challenge to an on premises agent that checks AD in real time.
- Yes No pattern: exam asks whether the named solution closes the stated gap, requiring mechanism fit.
Why A is correct
A is correct because pass through removes reliance on synced hash freshness for the authentication decision. Each sign in triggers on premises verification, so a just disabled user cannot present a valid password response. That directly meets the goal of immediate prevention after disable.
Why the others are wrong
- B. No would claim the gap remains, ignoring live on premises validation that closes it.
SC-300 exam tip
Immediate disable after AD change points to pass through live validation.
- Yes
- No
The short version
B — No, Conditional Access does not fix sync delay. Policy evaluates after identity proof, so disabled users still pass until directory sync catches up in the settled key.
Key concepts in this question
- Conditional Access scope: enforces MFA, device, location, and risk grants on top of a successful authentication.
- Authentication versus authorization: proving who you are precedes evaluating access rules, so AD disable must block the first step.
- Sync lag root cause: thirty minute password hash and account state delay lets disabled users authenticate briefly.
- Pass through contrast: live on premises check that actually closes the gap by validating each logon in real time.
- No pattern: correct when the proposal controls conditions but not the underlying stale credential acceptance.
Why B is correct
B is correct because Conditional Access policies assume the directory already rejected invalid principals before conditions apply. A disabled on premises account with a still valid cloud hash can satisfy primary auth and then meet policy grants. Since the solution does not force real time AD validation, it fails the immediate block goal.
Why the others are wrong
- A. Yes would wrongly claim access rules override stale authentication acceptance.
SC-300 exam tip
Sync delay disable gaps need live auth, not more access conditions.
- Yes
- No
The short version
B — No, password writeback does not block disabled accounts faster. It syncs cloud passwords down to on-prem for self-service reset. Immediate sign-in cut needs sync or auth handling, not writeback.
Key concepts in this question
- Password writeback: allows Entra password changes to flow to Active Directory for hybrid users.
- Disabled lag: synced disabled state can take time to reflect in cloud tokens and sessions.
- Real fix paths: password hash sync timing, pass-through auth, federation or conditional access session controls.
- Goal mismatch: writeback concerns credential update direction, not account enablement propagation.
- Series logic: each solution must be judged alone on whether it meets instant block.
Why B is correct
B is correct because configuring password writeback does nothing to revoke existing Entra sessions or hasten disabled propagation from Active Directory. Writeback writes cloud-initiated changes down, while the problem is upbound disablement still allowing auth for up to 30 minutes. Instant prevention needs faster sync, sign-in block handling or token lifetime controls. Since writeback leaves that path untouched, it fails the goal and the answer is No.
Why the others are wrong
- A. claims Yes, but writeback direction is opposite to disablement and cannot invalidate cloud tokens sooner.
SC-300 exam tip
Writeback equals cloud to on-prem passwords. Disable lag equals sync and session controls, never writeback.
Want the full bank of 461 questions for Microsoft Identity and Access Administrator (SC-300)? See all practice exams.