PCCSE — Free Practice Questions
10 free sample questions from a bank of 350, with the correct answers and explanations. No signup required — start practising right now.
1Given a default deployment of Console, a customer needs to identify the alerted compliance checks that are set by default.
Where should the customer navigate in Console?
- Monitor > Compliance
- Defend > Compliance
- Manage > Compliance
- Custom > Compliance
Answer: B
2A DevOps lead reviewed some system logs and notices some odd behavior that could be a data exfiltration attempt. The DevOps lead only has access to vulnerability data in Prisma Cloud Compute, so the DevOps lead passes this information to SecOps.
Which pages in Prisma Cloud Compute can the SecOps lead use to investigate the runtime aspects of this attack?
- The SecOps lead should investigate the attack using Vulnerability Explorer and Runtime Radar.
- The SecOps lead should use Incident Explorer and Compliance Explorer.
- The SecOps lead should use the Incident Explorer page and Monitor > Events > Container Audits.
- The SecOps lead should review the vulnerability scans in the CI/CD process to determine blame.
Answer: C
3An administrator sees that a runtime audit has been generated for a container.
The audit message is:
“/bin/ls launched and is explicitly blocked in the runtime rule. Full command: ls -latr”
Which protection in the runtime rule would cause this audit?
- Networking
- File systems
- Processes
- Container
Answer: C
4Which data security default policy is able to scan for vulnerabilities?
- Objects containing Vulnerabilities
- Objects containing Threats
- Objects containing Malware
- Objects containing Exploits
Answer: C
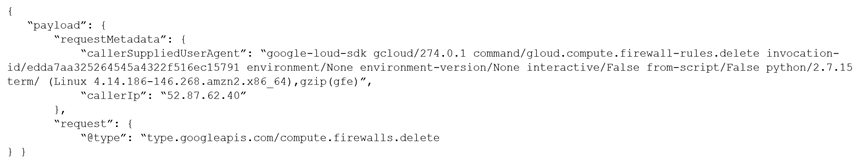
5Given the following audit event activity snippet: Which RQL will be triggered by the audit event?
Answer:
6Which three fields are mandatory when authenticating the Prisma Cloud plugin in the IntelliJ application? (Choose three.)
- Secret Key
- Prisma Cloud API URL
- Tags
- Access Key
- Asset Name
Answer:
7Which of the following are correct statements regarding the use of access keys? (Choose two.)
- Access keys must have an expiration date
- Up to two access keys can be active at any time
- System Admin can create access key for all users
- Access keys are used for API calls
Answer:
8Given the following RQL: Which audit event snippet is identified by the RQL?

Answer:
9The development team is building pods to host a web front end, and they want to protect these pods with an application firewall.
Which type of policy should be created to protect this pod from Layer7 attacks?
- The development team should create a WAAS rule for the host where these pods will be running.
- The development team should create a WAAS rule targeted at all resources on the host.
- The development team should create a runtime policy with networking protections.
- The development team should create a WAAS rule targeted at the image name of the pods.
Answer: D
10A manager informs the SOC that one or more RDS instances have been compromised and the SOC needs to make sure production RDS instances are NOT publicly accessible.
Which action should the SOC take to follow security best practices?
- Enable “AWS S3 bucket is publicly accessible” policy and manually remediate each alert.
- Enable “AWS RDS database instance is publicly accessible” policy and for each alert, check that it is a production instance, and then manually remediate.
- Enable “AWS S3 bucket is publicly accessible” policy and add policy to an auto-remediation alert rule.
- Enable “AWS RDS database instance is publicly accessible” policy and add policy to an auto-remediation alert rule.
Answer: D
Want the full bank of 350 questions for PCCSE? See all practice exams.