NSE7_SDW-6.4 — Free Practice Questions
10 free sample questions from a bank of 74, with the correct answers and explanations. No signup required — start practising right now.
1Refer to the exhibit. Multiple IPsec VPNs are formed between two hub-and-spokes groups, and site-to-site between Hub 1 and Hub 2. The administrator configured ADVPN on the dual regions topology.
Which two statements are correct if a user in Toronto sends traffic to London? (Choose two.)
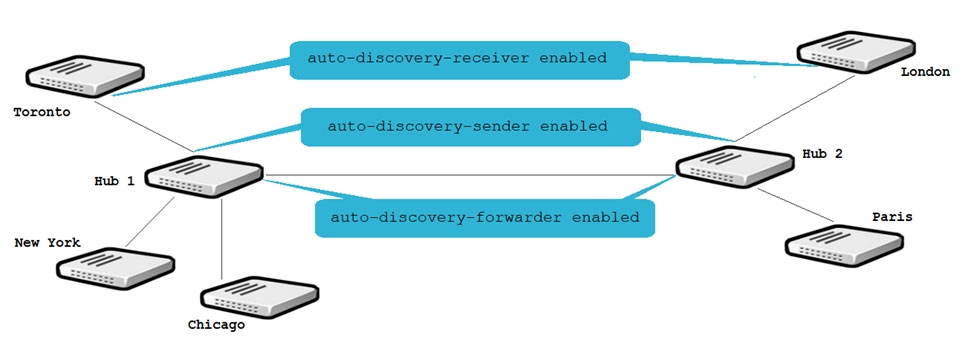
- Toronto needs to establish a site-to-site tunnel with Hub 2 to bypass Hub 1.
- The first packets from Toronto to London are routed through Hub 1 then to Hub 2.
- London generates an IKE information message that contains the Toronto public IP address.
- Traffic from Toronto to London triggers the dynamic negotiation of a direct site-to-site VPN.
Answer:
2Refer to exhibits. Exhibit A shows the source NAT global setting and exhibit B shows the routing table on FortiGate.
Based on the exhibits, which two statements about increasing the port2 interface priority to 20 are true? (Choose two.)
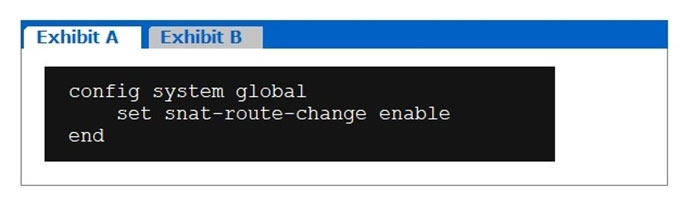
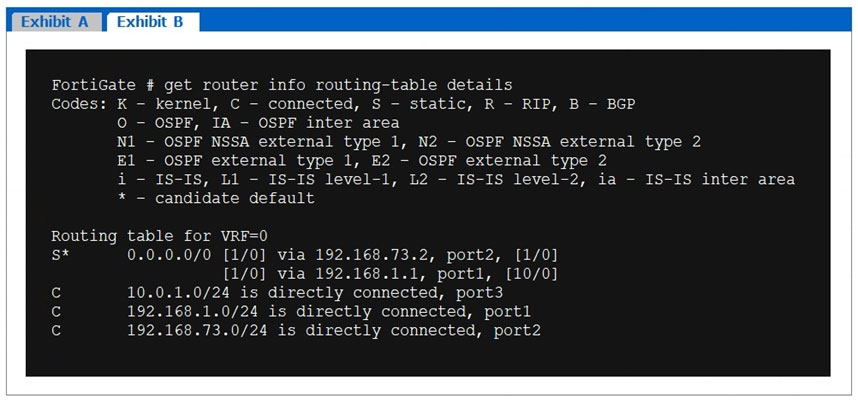
- All the existing sessions that do not use SNAT will be flushed and routed through port1.
- All the existing sessions will continue to use port2, and new sessions will use port1.
- All the existing sessions using SNAT will be flushed and routed through port1.
- All the existing sessions will be blocked from using port1 and port2.
Answer:
3Which components make up the secure SD-WAN solution?
- FortiGate, FortiManager, FortiAnalyzer, and FortiDeploy
- Application, antivirus, and URL, and SSL inspection
- Datacenter, branch offices, and public cloud
- Telephone, ISDN, and telecom network
Answer: A
4Refer to the exhibit. Which two statements about the status of the VPN tunnel are true? (Choose two.)
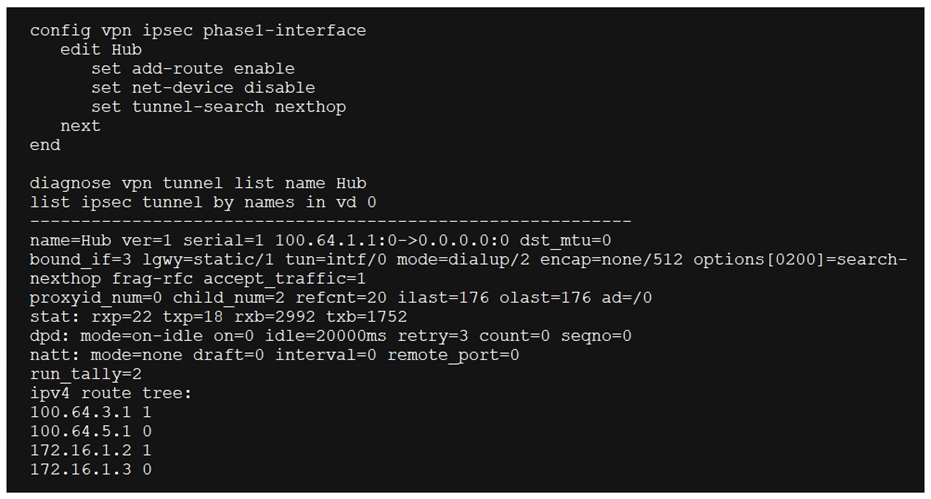
- There are separate virtual interfaces for each dial-up client.
- VPN static routes are prevented from populating the FortiGate routing table.
- FortiGate created a single IPsec virtual interface that is shared by all clients.
- 100.64.3.1 is one of the remote IP address that comes through index interface 1.
Answer:
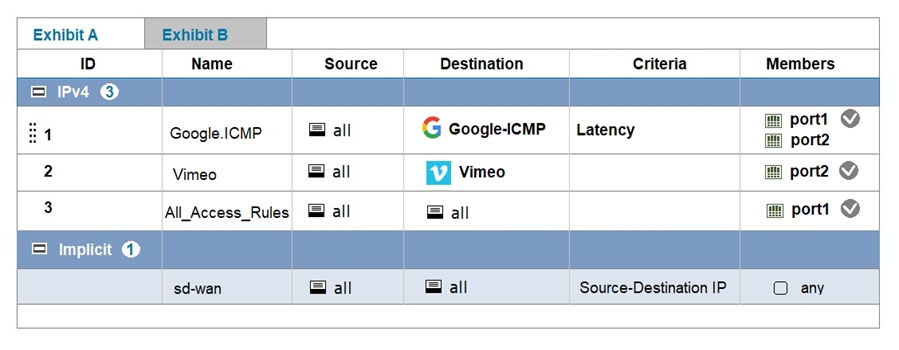
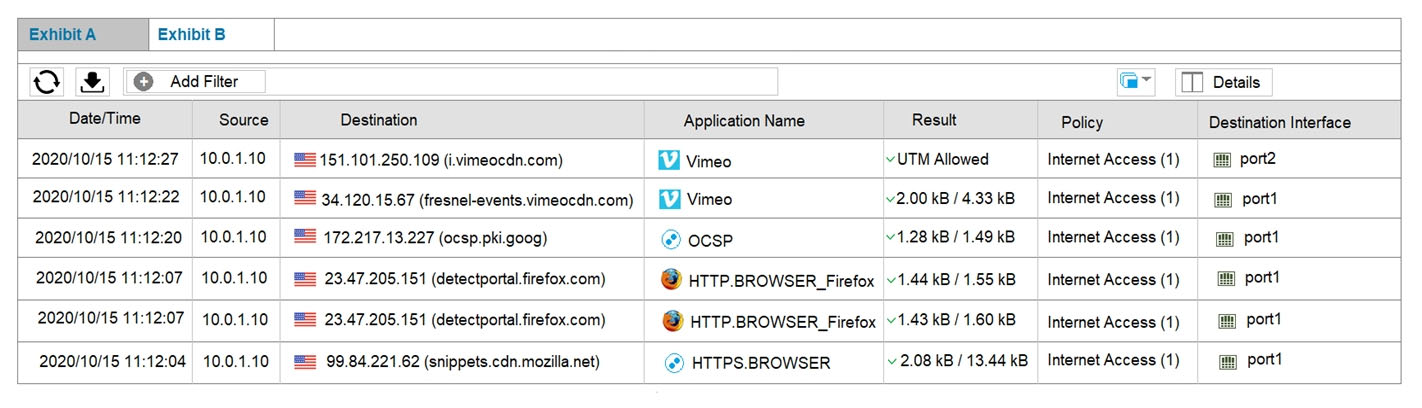
5Refer to exhibits. Exhibit A shows the SD-WAN rules and exhibit B shows the traffic logs. The SD-WAN traffic logs reflect how FortiGate processed traffic.
Which two statements about how the configured SD-WAN rules are processing traffic are true? (Choose two.)
- The implicit rule overrides all other rules because parameters widely cover sources and destinations.
- SD-WAN rules are evaluated in the same way as firewall policies: from top to bottom.
- The All_Access_Rules rule load balances Vimeo application traffic among SD-WAN member interfaces.
- The initial session of an application goes through a learning phase in order to apply the correct rule.
Answer:
6What are the two minimum configuration requirements for an outgoing interface to be selected once the SD-WAN logical interface is enabled? (Choose two.)
- Specify outgoing interface routing cost.
- Configure SD-WAN rules interface preference.
- Select SD-WAN balancing strategy.
- Specify incoming interfaces in SD-WAN rules.
Answer:
7Refer to the exhibit. Based on the exhibit, which statement about FortiGate re-evaluating traffic is true?
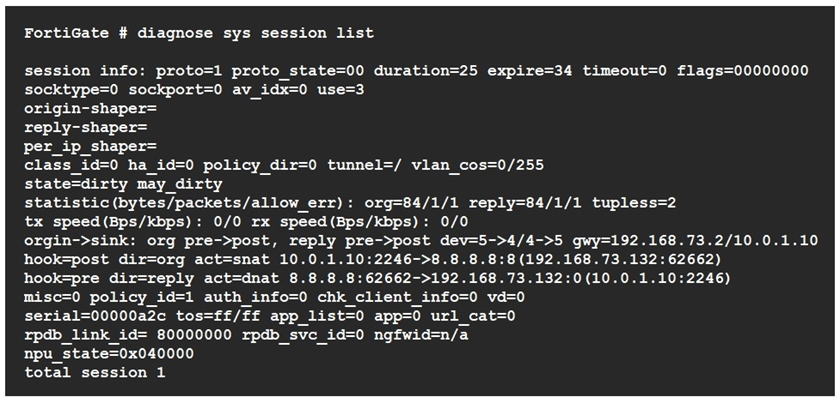
- The type of traffic defined and allowed on firewall policy ID 1 is UDP.
- Changes have been made on firewall policy ID 1 on FortiGate.
- Firewall policy ID 1 has source NAT disabled.
- FortiGate has terminated the session after a change on policy ID 1.
Answer: B
8What are two reasons why FortiGate would be unable to complete the zero-touch provisioning process? (Choose two.)
- The FortiGate cloud key has not been added to the FortiGate cloud portal.
- FortiDeploy has connected with FortiGate and provided the initial configuration to contact FortiManager.
- FortiGate has obtained a configuration from the platform template in FortiGate cloud.
- A factory reset performed on FortiGate.
- The zero-touch provisioning process has completed internally, behind FortiGate.
Answer:
9Which two statements reflect the benefits of implementing the ADVPN solution to replace conventional VPN topologies? (Choose two.)
- It creates redundant tunnels between hub-and-spokes, in case failure takes place on the primary links.
- It dynamically assigns cost and weight between the hub and the spokes, based on the physical distance.
- It ensures that spoke-to-spoke traffic no longer needs to flow through the tunnels through the hub.
- It provides direct connectivity between all sites by creating on-demand tunnels between spokes.
Answer:
10Refer to the exhibit. Based on the output shown in the exhibit, which two criteria on the SD-WAN member configuration can be used to select an outgoing interface in an SD-WAN rule? (Choose two.)
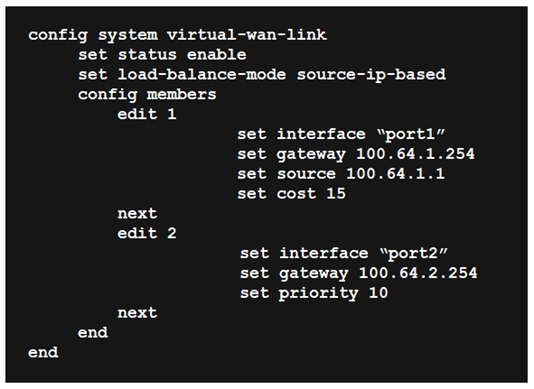
- set cost 15.
- set source 100.64.1.1.
- set priority 10.
- set load-balance-mode source-ip-based.
Answer:
Want the full bank of 74 questions for NSE7_SDW-6.4? See all practice exams.