NSE7 — Free Practice Questions
10 free sample questions from a bank of 80, with the correct answers and explanations. No signup required — start practising right now.
1A FortiGate device has the following LDAP configuration:
config user ldap
edit "WindowsLDAP"
set server "10.0.1.10"
set cnid "cn"
set dn "cn=Users, dc=trainingAD, dc=training, dc=lab"
set type regular
set username "dc=trainingAD, dc=training, dc=lab"
set password xxxxxxx
next
end
The administrator executed the 'dsquery' command in the Windows LDAP server 10.0.1.10, and got the following output:
>dsquery user -samid administrator
"CN=Administrator, CN=Users, DC=trainingAD, DC=training, DC=lab"
Based on the output, what FortiGate LDAP setting is configured incorrectly?
- cnid.
- username.
- password.
- dn.
Answer: A
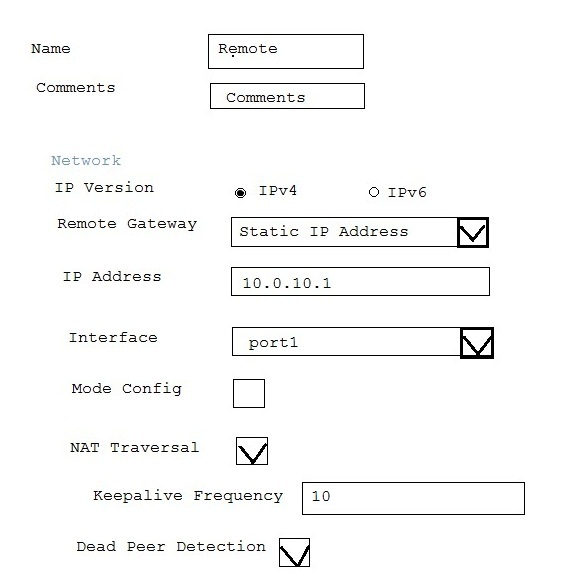
2Examine the IPsec configuration shown in the exhibit; then answer the question below. An administrator wants to monitor the VPN by enabling the IKE real time debug using these commands: diagnose vpn ike log-filter src-addr4 10.0.10.1 diagnose debug application ike -1 diagnose debug enable
The VPN is currently up, there is no traffic crossing the tunnel and DPD packets are being interchanged between both IPsec gateways. However, the IKE real time debug does NOT show any output. Why isn't there any output?
- The IKE real time shows the phases 1 and 2 negotiations only. It does not show any more output once the tunnel is up.
- The log-filter setting is set incorrectly. The VPN's traffic does not match this filter.
- The IKE real time debug shows the phase 1 negotiation only. For information after that, the administrator must use the IPsec real time debug instead: diagnose debug application ipsec -1.
- The IKE real time debug shows error messages only. If it does not provide any output, it indicates that the tunnel is operating normally.
Answer: B
3Examine the output of the "˜get router info bgp summary' command shown in the exhibit; then answer the question below. Which statements are true regarding the output in the exhibit? (Choose two.)
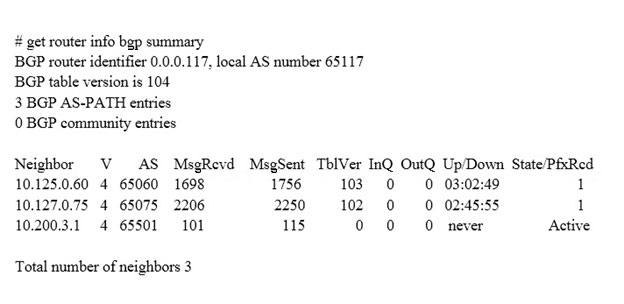
- BGP state of the peer 10.125.0.60 is Established.
- BGP peer 10.200.3.1 has never been down since the BGP counters were cleared.
- Local BGP peer has not received an OpenConfirm from 10.200.3.1.
- The local BGP peer has received a total of 3 BGP prefixes.
Answer:
4Examine the following partial output from a sniffer command; then answer the question below. What is the meaning of the packets dropped counter at the end of the sniffer?
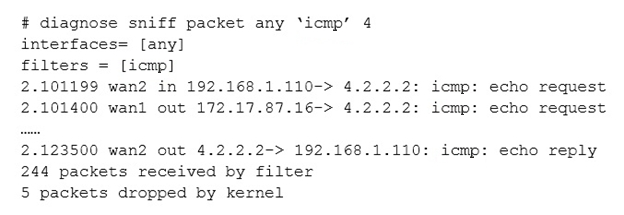
- Number of packets that didn't match the sniffer filter.
- Number of total packets dropped by the FortiGate.
- Number of packets that matched the sniffer filter and were dropped by the FortiGate.
- Number of packets that matched the sniffer filter but could not be captured by the sniffer.
Answer: D
5A FortiGate is configured as an explicit web proxy. Clients using this web proxy are reposting DNS errors when accessing any website. The administrator executes the following debug commands and observes that the n-dns-timeout counter is increasing: What should the administrator check to fix the problem?
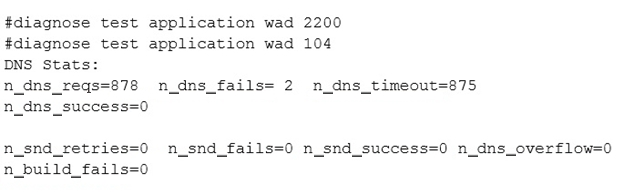
- The connectivity between the FortiGate unit and the DNS server.
- The connectivity between the client workstations and the DNS server.
- That DNS traffic from client workstations is allowed by the explicit web proxy policies.
- That DNS service is enabled in the explicit web proxy interface.
Answer: A
6Which real time debug should an administrator enable to troubleshoot RADIUS authentication problems?
- Diagnose debug application radius -1.
- Diagnose debug application fnbamd -1.
- Diagnose authd console ""log enable.
- Diagnose radius console ""log enable.
Answer: B
7Examine the output of the "˜diagnose sys session list expectation' command shown in the exhibit; than answer the question below. Which statement is true regarding the session in the exhibit?
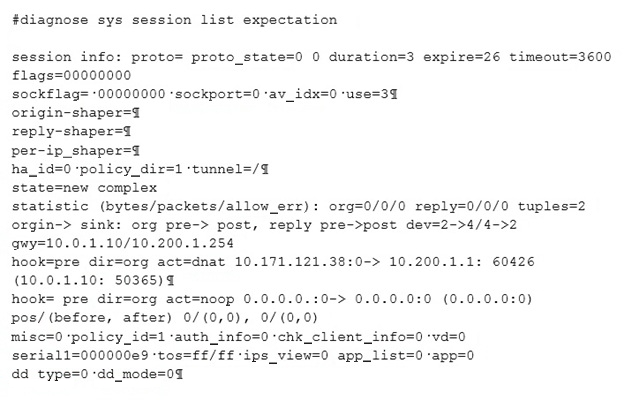
- It was created by the FortiGate kernel to allow push updates from FotiGuard.
- It is for management traffic terminating at the FortiGate.
- It is for traffic originated from the FortiGate.
- It was created by a session helper or ALG.
Answer: D
8An administrator has configured a FortiGate device with two VDOMs: root and internal. The administrator has also created and inter-VDOM link that connects both
VDOMs. The objective is to have each VDOM advertise some routes to the other VDOM via OSPF through the inter-VDOM link. What OSPF configuration settings must match in both VDOMs to have the OSPF adjacency successfully forming? (Choose three.)
- Router ID.
- OSPF interface area.
- OSPF interface cost.
- OSPF interface MTU.
- Interface subnet mask.
Answer:
9An administrator has configured a dial-up IPsec VPN with one phase 2, extended authentication (XAuth) and IKE mode configuration. The administrator has also enabled the IKE real time debug: diagnose debug application ike-1 diagnose debug enable
In which order is each step and phase displayed in the debug output each time a new dial-up user is connecting to the VPN?
- Phase1; IKE mode configuration; XAuth; phase 2.
- Phase1; XAuth; IKE mode configuration; phase2.
- Phase1; XAuth; phase 2; IKE mode configuration.
- Phase1; IKE mode configuration; phase 2; XAuth.
Answer: B
10Two independent FortiGate HA clusters are connected to the same broadcast domain. The administrator has reported that both clusters are using the same HA virtual MAC address. This creates a duplicated MAC address problem in the network. What HA setting must be changed in one of the HA clusters to fix the problem?
- Group ID.
- Group name.
- Session pickup.
- Gratuitous ARPs.
Answer: A
Want the full bank of 80 questions for NSE7? See all practice exams.