NSE4_FGT-6.4 — Free Practice Questions
10 free sample questions from a bank of 118, with the correct answers and explanations. No signup required — start practising right now.
1Which two statements are true when FortiGate is in transparent mode? (Choose two.)
- By default, all interfaces are part of the same broadcast domain.
- The existing network IP schema must be changed when installing a transparent mode FortiGate in the network.
- Static routes are required to allow traffic to the next hop.
- FortiGate forwards frames without changing the MAC address.
Answer: A, D
2What is the effect of enabling auto-negotiate on the phase 2 configuration of an IPsec tunnel?
- FortiGate automatically negotiates different local and remote addresses with the remote peer.
- FortiGate automatically negotiates a new security association after the existing security association expires.
- FortiGate automatically negotiates different encryption and authentication algorithms with the remote peer.
- FortiGate automatically brings up the IPsec tunnel and keeps it up, regardless of activity on the IPsec tunnel.
Answer: D
3An administrator wants to configure Dead Peer Detection (DPD) on IPSEC VPN for detecting dead tunnels. The requirement is that FortiGate sends DPD probes only when no traffic is observed in the tunnel.
Which DPD mode on FortiGate will meet the above requirement?
- Disabled
- On Demand
- Enabled
- On Idle
Answer: D
4Refer to the exhibit. Based on the administrator profile settings, what permissions must the administrator set to run the diagnose firewall auth list CLI command on
FortiGate?
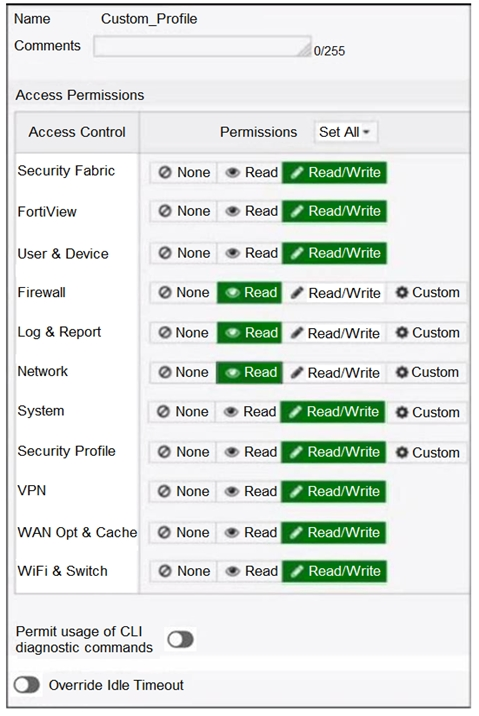
- Read/Write permission for Firewall
- Custom permission for Network
- Read/Write permission for Log & Report
- CLI diagnostics commands permission
Answer: B
5In an explicit proxy setup, where is the authentication method and database configured?
- Proxy Policy
- Authentication Rule
- Firewall Policy
- Authentication scheme
Answer: D
6Refer to the exhibit. Given the routing database shown in the exhibit, which two statements are correct? (Choose two.)
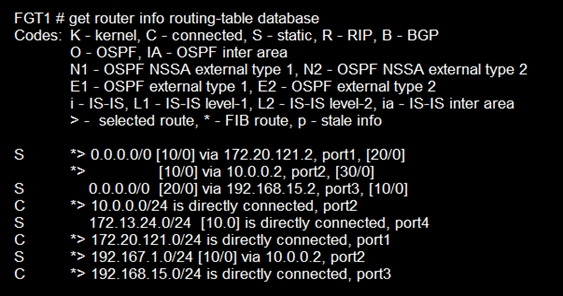
- The port3 default route has the lowest metric
- The port3 default route has the highest distance
- The port1 and port2 default routes are active in the routing table
- There will be eight routes active in the routing table
Answer: B, C
7Which three statements about a flow-based antivirus profile are correct? (Choose three.)
- Flow-based inspection uses a hybrid of scanning modes available in proxy-based inspection
- Optimized performance compared to proxy-based inspection
- FortiGate buffers the whole file but transmits for the client simultaneously
- If the virus is detected, the last packet is delivered to the client
- IPS engine handles the process as a standalone
Answer: A, B, C
8Refer to the exhibit. The exhibit shows a CLI output of firewall policies, proxy policies, and proxy addresses.
How does FortiGate process the traffic sent to http://www.fortinet.com?
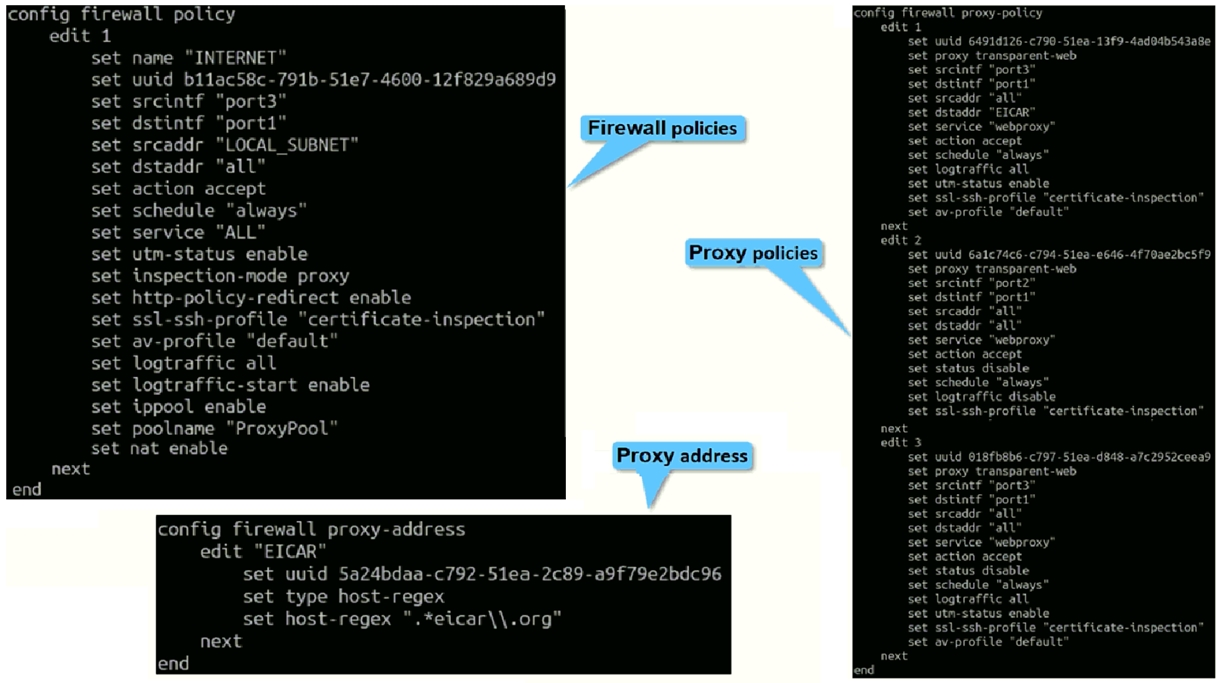
- Traffic will be redirected to the transparent proxy and it will be denied by the proxy implicit deny policy.
- Traffic will be redirected to the transparent proxy and it will be allowed by proxy policy ID 3.
- Traffic will not be redirected to the transparent proxy and it will be allowed by firewall policy ID 1.
- Traffic will be redirected to the transparent proxy and it will be allowed by proxy policy ID 1.
Answer: A
9Which two protocol options are available on the CLI but not on the GUI when configuring an SD-WAN Performance SLA? (Choose two.)
- udp-echo
- DNS
- TWAMP
- ping
Answer: A, C
10Which two inspection modes can you use to configure a firewall policy on a profile-based next-generation firewall (NGFW)? (Choose two.)
- Proxy-based inspection
- Certificate inspection
- Flow-based inspection
- Full Content inspection
Answer: A, C
Want the full bank of 118 questions for NSE4_FGT-6.4? See all practice exams.