NSE4_FGT-6.0 — Free Practice Questions
10 free sample questions from a bank of 126, with the correct answers and explanations. No signup required — start practising right now.
1What files are sent to FortiSandbox for inspection in flow-based inspection mode?
- All suspicious files that do not have their hash value in the FortiGuard antivirus signature database.
- All suspicious files that are above the defined oversize limit value in the protocol options.
- All suspicious files that match patterns defined in the antivirus profile.
- All suspicious files that are allowed to be submitted to FortiSandbox in the antivirus profile.
Answer: C
2View the exhibit. Based on this output, which statements are correct? (Choose two.)
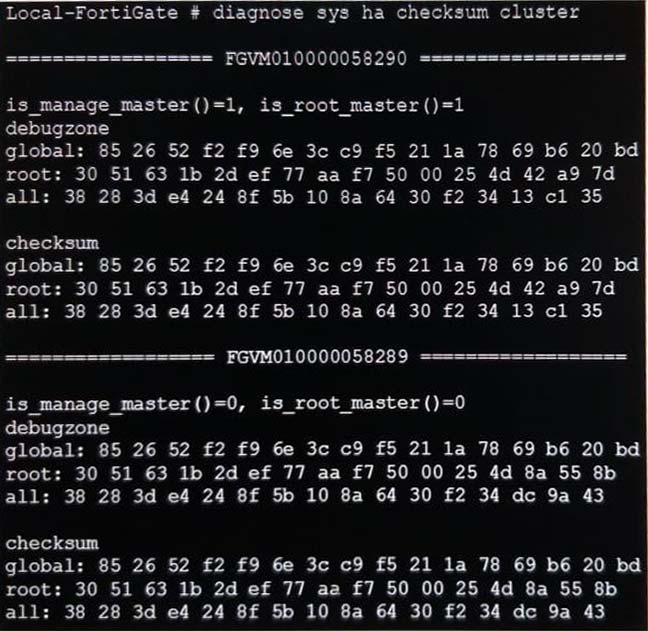
- The all VDOM is not synchronized between the primary and secondary FortiGate devices.
- The root VDOM is not synchronized between the primary and secondary FortiGate devices.
- The global configuration is synchronized between the primary and secondary FortiGate devices.
- The FortiGate devices have three VDOMs.
Answer: B, C
3When using WPAD DNS method, which FQDN format do browsers use to query the DNS server?
- srv_proxy. /wpad.dat
- srv_tcp.wpad.
- wpad.
- proxy. .wpad
Answer: C
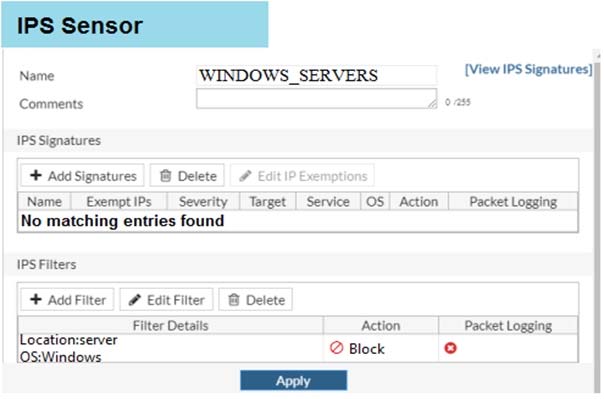
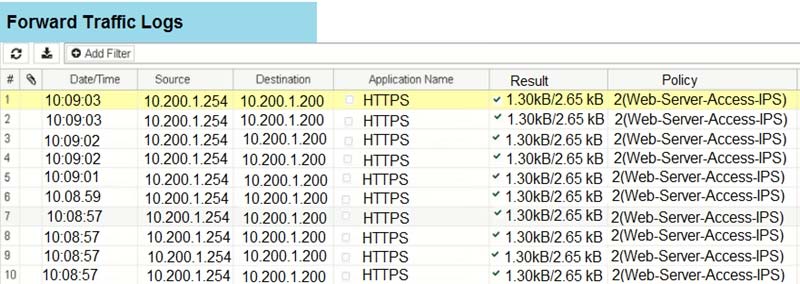
4Examine the IPS sensor configuration shown in the exhibit, and then answer the question below. An administrator has configured the WINDOS_SERVERS IPS sensor in an attempt to determine whether the influx of HTTPS traffic is an attack attempt or not. After applying the IPS sensor, FortiGate is still not generating any IPS logs for the HTTPS traffic.
What is a possible reason for this?
- The IPS filter is missing the Protocol: HTTPS option.
- The HTTPS signatures have not been added to the sensor.
- A DoS policy should be used, instead of an IPS sensor.
- A DoS policy should be used, instead of an IPS sensor.
- The firewall policy is not using a full SSL inspection profile.
Answer: E
5What types of traffic and attacks can be blocked by a web application firewall (WAF) profile? (Choose three.)
- Traffic to botnetservers
- Traffic to inappropriate web sites
- Server information disclosure attacks
- Credit card data leaks
- SQL injection attacks
Answer: A, C, E
6Which statement about DLP on FortiGate is true?
- It can archive files and messages.
- It can be applied to a firewall policy in a flow-based VDOM
- Traffic shaping can be applied to DLP sensors.
- Files can be sent to FortiSandbox for detecting DLP threats.
Answer: A
7Examine this PAC file configuration. Which of the following statements are true? (Choose two.)
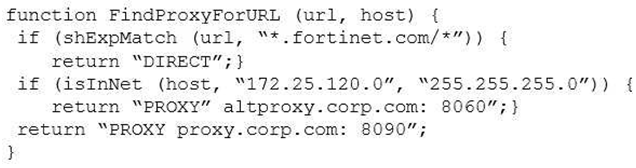
- Browsers can be configured to retrieve this PAC file from the FortiGate.
- Any web request to the 172.25.120.0/24 subnet is allowed to bypass the proxy.
- All requests not made to Fortinet.com or the 172.25.120.0/24 subnet, have to go through altproxy.corp.com: 8060.
- Any web request fortinet.com is allowed to bypass the proxy.
Answer: A, D
8Which statements about the firmware upgrade process on an active-active HA cluster are true? (Choose two.)
- The firmware image must be manually uploaded to each FortiGate.
- Only secondary FortiGate devices are rebooted.
- Uninterruptable upgrade is enabled by default.
- Traffic load balancing is temporally disabled while upgrading the firmware.
Answer: B, D
9Which statements best describe auto discovery VPN (ADVPN). (Choose two.)
- It requires the use of dynamic routing protocols so that spokes can learn the routes to other spokes.
- ADVPN is only supported with IKEv2.
- Tunnels are negotiated dynamically between spokes.
- Every spoke requires a static tunnel to be configured to other spokes so that phase 1 and phase 2 proposals are defined in advance.
Answer: A, C
10An administrator needs to create an SSL-VPN connection for accessing an internal server using the bookmark Port Forward. What step is required for this configuration?
- Configure an SSL VPN realm for clients to use the port forward bookmark.
- Configure the client application to forward IP traffic through FortiClient.
- Configure the virtual IP address to be assigned t the SSL VPN users.
- Configure the client application to forward IP traffic to a Java applet proxy.
Answer: D
Want the full bank of 126 questions for NSE4_FGT-6.0? See all practice exams.