NSE4-5.4 — Free Practice Questions
10 free sample questions from a bank of 62, with the correct answers and explanations. No signup required — start practising right now.
1An administrator observes that the port1 interface cannot be configured with an IP address. What can be the reasons for that? (Choose three.)
- The interface has been configured for one-arm sniffer.
- The interface is a member of a virtual wire pair.
- The operation mode is transparent.
- The interface is a member of a zone.
- Captive portal is enabled in the interface.
Answer:
2Examine the following web filtering log. Which statement about the log message is true?
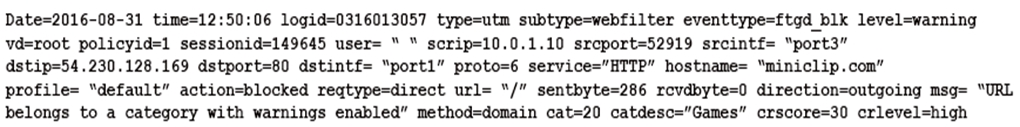
- The action for the category Games is set to block.
- The usage quota for the IP address 10.0.1.10 has expired.
- The name of the applied web filter profile is default.
- The web site miniclip.com matches a static URL filter whose action is set to Warning.
Answer: D
3Examine this output from a debug flow: Which statements about the output are correct? (Choose two.)
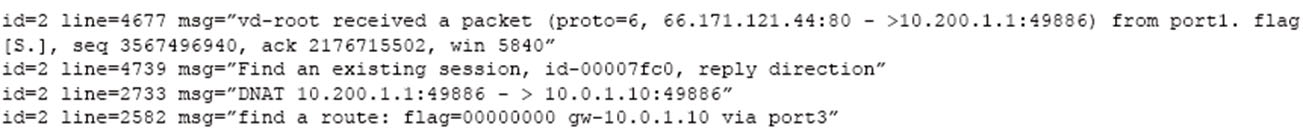
- The packet was allowed by the firewall policy with the ID 00007fc0.
- FortiGate routed the packet through port3.
- FortiGate received a TCP SYN/ACK packet.
- The source IP address of the packet was translated to 10.0.1.10.
Answer:
4View the exhibit. Which users and user groups are allowed access to the network through captive portal?
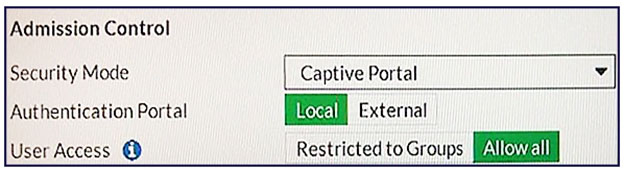
- Only individual usersג€"not groupsג€"defined in the captive portal configuration.
- Groups defined in the captive portal configuration
- All users
- Users and groups defined in the firewall policy.
Answer: A
5An administrator needs to create a tunnel mode SSLVPN to access an internal web server from the Internet. The web server is connected to port1. The Internet is connected to port2. Both interfaces belong to the VDOM named Corporation. What interface must be used as the source for the firewall policy that will allow this traffic?
- ssl.root
- ssl.Corporation
- port2
- port1
Answer: C
6View the exhibit. Why is the administrator getting the error shown in the exhibit?
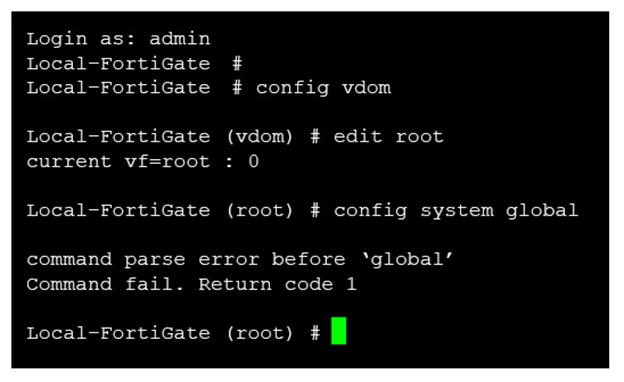
- The administrator admin does not have the privileges required to configure global settings.
- The global settings cannot be configured from the root VDOM context.
- The command config system global does not exist in FortiGate.
- The administrator must first enter the command edit global.
Answer: A
7What FortiGate feature can be used to block a ping sweep scan from an attacker?
- Web application firewall (WAF)
- Rate based IPS signatures
- One-arm sniffer
- DoS policies
Answer: B
8Which statements about the firmware upgrade process on an active-active high availability (HA) cluster are true? (Choose two.)
- The firmware image must be manually uploaded to each FortiGate.
- Only secondary FortiGate devices are rebooted.
- Uninterruptable upgrade is enabled by default.
- Traffic load balancing is temporally disabled while upgrading the firmware.
Answer:
9View the example routing table. Which route will be selected when trying to reach 10.20.30.254?
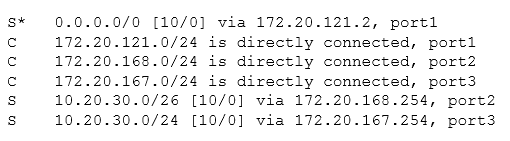
- 10.20.30.0/26 [10/0] via 172.20.168.254, port2
- The traffic will be dropped because it cannot be routed.
- 10.20.30.0/24 [10/0] via 172.20.167.254, port3
- 0.0.0.0/0 [10/0] via 172.20.121.2, port1
Answer: C
10View the exhibit. Which statements are correct, based on this output? (Choose two.)
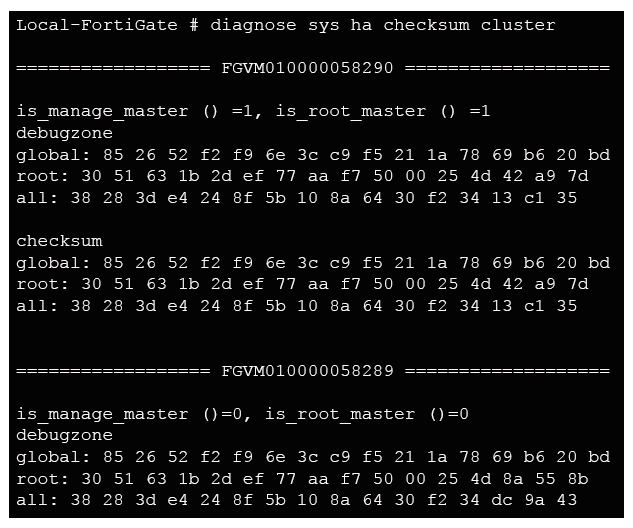
- The FortiGate have three VDOMs.
- The all VDOM is not synchronized between the primary and secondary FortiGate.
- The global configuration is synchronized between the primary and secondary FortiGate.
- The root VDOM is not synchronized between the primary and secondary FortiGate.
Answer:
Want the full bank of 62 questions for NSE4-5.4? See all practice exams.