300-209 — Free Practice Questions
10 free sample questions from a bank of 55, with the correct answers and explanations. No signup required — start practising right now.
1Which two are characteristics of GETVPN? (Choose two.)
- The IP header of the encrypted packet is preserved
- A key server is elected among all configured Group Members
- Unique encryption keys are computed for each Group Member
- The same key encryption and traffic encryption keys are distributed to all Group Members
Answer:
2Which transform set is contained in the IKEv2 default proposal?
- aes-cbc-192, sha256, group 14
- 3des, md5, group 7
- 3des, sha1, group 1
- aes-cbc-128, sha, group 5
Answer: D
3The following configuration steps have been completeD.
✑ WebVPN was enabled on the ASA outside interface.
✑ SSL VPN client software was loaded to the ASA.
✑ A DHCP scope was configured and applied to a WebVPN Tunnel Group.
What additional step is required if the client software fails to load when connecting to the ASA SSL page?
- The SSL client must be loaded to the client by an ASA administrator
- The SSL client must be downloaded to the client via FTP
- The SSL VPN client must be enabled on the ASA after loading
- The SSL client must be enabled on the client machine before loading
Answer: A
4Refer to the exhibit. Which statement about the given IKE policy is true?
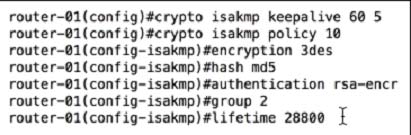
- The tunnel will be valid for 2 days, 88 minutes, and 00 seconds.
- It will use encrypted nonces for authentication.
- It has a keepalive of 60 minutes, checking every 5 minutes.
- It uses a 56-bit encryption algorithm.
Answer: B
5In which situation would you enable the Smart Tunnel option with clientless SSL VPN?
- when a user is using an outdated version of a web browser
- when an application is failing in the rewrite process
- when IPsec should be used over SSL VPN
- when a user has a nonsupported Java version installed
- when cookies are disabled
Answer: B
6Where do you configure AnyConnect certificate-based authentication in ASDM?
- group policies
- AnyConnect Connection Profile
- AnyConnect Client Profile
- Advanced Network (Client) Access
Answer: B
7Refer to the exhibit. Which VPN solution does this configuration represent?
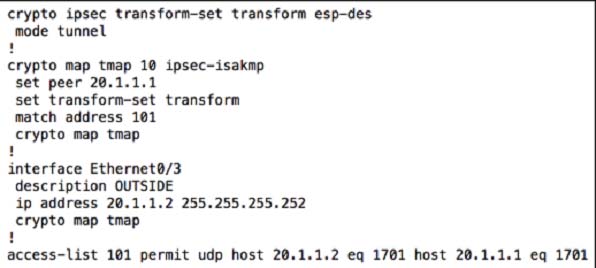
- Cisco AnyConnect
- IPsec
- L2TP
- SSL VPN
Answer: B
8In the Diffie-Hellman protocol, which type of key is the shared secret?
- a symmetric key
- an asymmetric key
- a decryption key
- an encryption key
Answer: A
9SIMULATION -
Scenario:
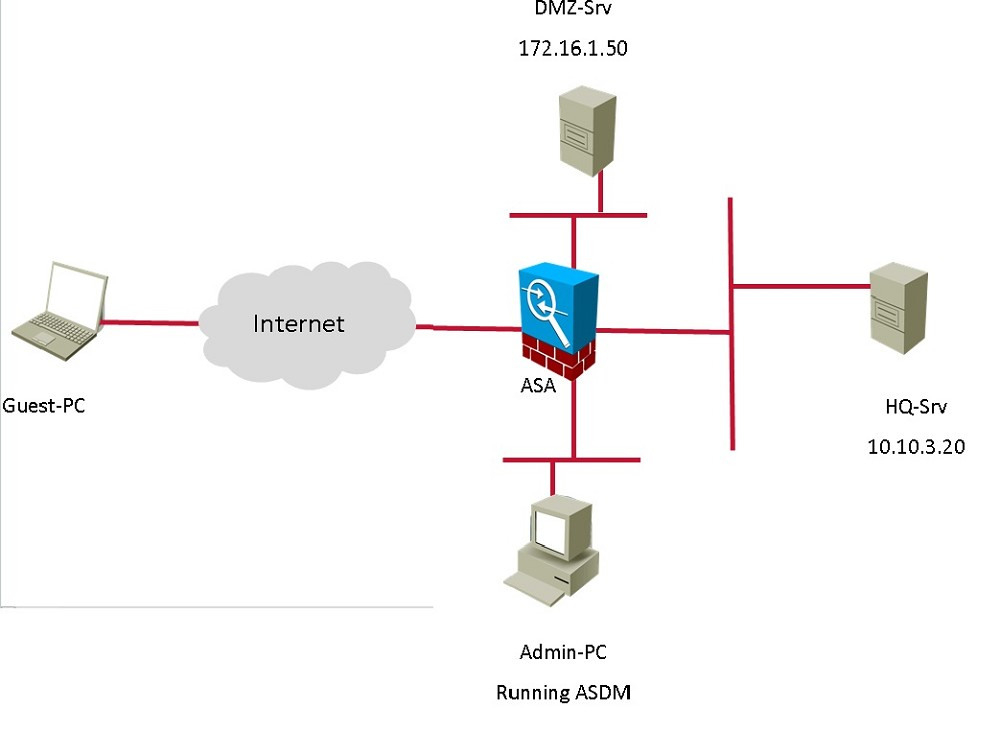
You are the network security manager for your organization. Your manager has received a request to allow an external user to access to your HQ and DM2 servers. You are given the following connection parameters for this task.
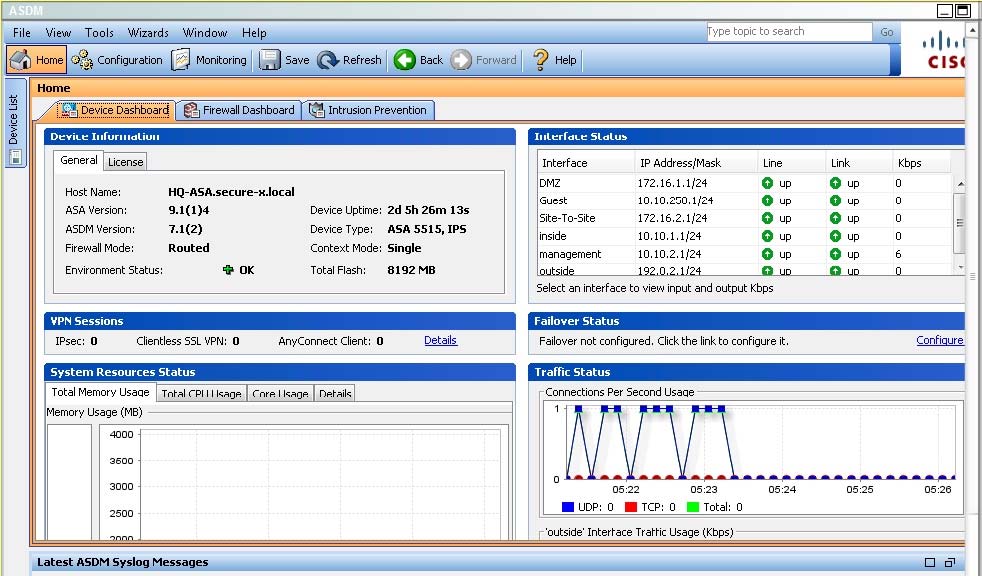
Using ASDM on the ASA, configure the parameters below and test your configuration by accessing the Guest PC. Not all AS DM screens are active for this exercise. Also, for this exercise, all changes are automatically applied to the ASA and you will not have to click APPLY to apply the changes manually.
Enable Clientless SSL VPN on the outside interface
Using the Guest PC, open an Internet Explorer window and test and verify the basic connection to the SSL VPN portal using address: https://vpn-secure- x.public
a. You may notice a certificate error in the status bar, this can be ignored for this exercise
b. Username: vpnuser
c. Password: cisco123
d. Logout of the portal once you have verified connectivity
Configure two bookmarks with the following parameters:
a. Bookmark List Name: MY-BOOKMARKS
b. Use the: URL with GET or POST method
c. Bookmark Title: HQ-Server
i. http://10.10.3.20
d. Bookmark Title: DMZ-Server-FTP
i. ftp://172.16.1.50
e. Assign the configured Bookmarks to:
i. DfltGrpPolicy
ii. DfltAccessPolicy
iii. LOCAL User: vpnuser
From the Guest PC, reconnect to the SSL VPN Portal
Test both configured Bookmarks to ensure desired connectivity
You have completed this exercise when you have configured and successfully tested Clientless SSL VPN connectivity.
Topology:
Answer:
10Scenario:
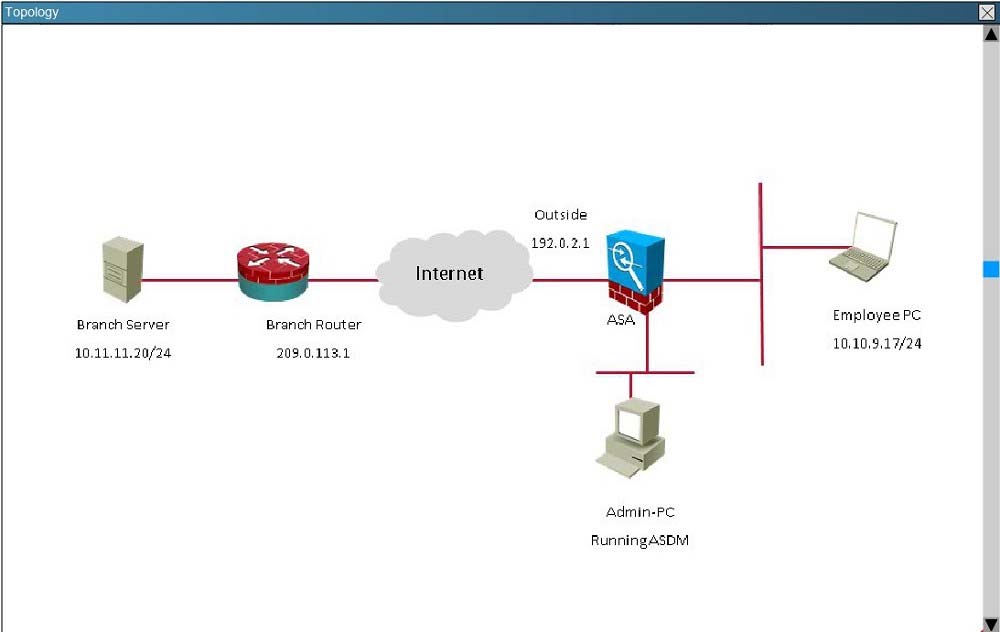
You are the senior network security administrator for your organization. Recently and junior engineer configured a site-to-site IPsec VPN connection between your headquarters Cisco ASA and a remote branch office.
You are now tasked with verifying the IKEvl IPsec installation to ensure it was properly configured according to designated parameters. Using the CLI on both the
Cisco ASA and branch ISR, verify the IPsec configuration is properly configured between the two sites.
NOTE: the show running-config command cannot be used for this exercise.
Topology: Which transform set is being used on the branch ISR?
- Default
- ESP-3DES ESP-SHA-HMAC
- ESP-AES-256-MD5-TRANS mode transport
- TSET
Answer: B
Want the full bank of 55 questions for 300-209? See all practice exams.