VMware Spring Professional (2V0-72.22) — Free Practice Questions
10 free sample questions from a bank of 77, with the correct answers and explanations. No signup required — start practising right now.
- Ensure a valid bean name in the @Component annotation is specified.
- Ensure a valid @ComponentScan annotation in the Java configuration is specified.
- Ensure a valid @Scope for the class is specified.
- Ensure a valid @Bean for the class is specified.
The short version
Answer B - @Component classes are picked up by component scanning via @ComponentScan.
Key concepts in this question
- Stereotype annotations and component scanning
- @Configuration plus @ComponentScan base packages
- Bean registration without explicit @Bean methods
Why B is correct
@ComponentScan enables autodetection of @Component, @Service, @Repository and @Controller classes and registers them as beans.
Why the others are wrong
- A: Bean name is optional; default name is generated, it does not enable scanning.
- C: @Scope only declares scope; it does not enable detection.
- D: @Bean is for explicit factory methods, not needed for autodetected components and does not enable scanning.
2V0-7222 exam tip
If you see @Component plus automatic detection, choose @ComponentScan; @Bean is the manual alternative.
- @Autowired public void setFoo (Foo foo) {…}
- @Autowired @Qualifier (“foo3”) Foo foo;
- @Autowired public void setFoo (@Qualifier (“foo1”) Foo foo) {…}
- @Autowired private Foo foo;
- @Autowired private Foo foo2;
- @Autowired public void setFoo(Foo foo2) {…}
The short version
Answers B, C, E - disambiguate three Foo beans with @Qualifier or matching field name.
Key concepts in this question
- @Autowired by type with multiple candidates
- @Qualifier for selection
- Field name fallback matching bean id
Why BCE is correct
B uses @Qualifier foo3 on a field, C uses @Qualifier foo1 on a setter parameter, E uses field name foo2 matching bean id foo2; each resolves to a single bean.
Why the others are wrong
- A: setFoo(Foo foo) with no qualifier and generic name cannot choose among foo1, foo2, foo3, so it fails.
- D: private Foo foo with no qualifier and generic name is ambiguous with three candidates.
- F: setFoo(Foo foo2) without @Qualifier is still ambiguous by type; parameter-name fallback alone is not relied upon here, and duplicate setFoo signature also conflicts with C.
2V0-7222 exam tip
Three beans of one type need @Qualifier or exact field-name match; plain by-type injection fails.
- spring-boot-devtools
- spring-boot-initializr
- spring-boot-starter-devtools
- spring-boot-restart
The short version
Answer A - spring-boot-devtools gives automatic restart during development.
Key concepts in this question
- Spring Boot devtools
- Automatic restart vs reload
- Dev-only dependency
Why A is correct
spring-boot-devtools provides automatic application restart when classpath code changes, intended for development.
Why the others are wrong
- B: spring-boot-initializr is a project generator web tool, not a restart dependency.
- C: spring-boot-starter-devtools is not the canonical artifact name; the dependency is spring-boot-devtools.
- D: spring-boot-restart is not a real dependency.
2V0-7222 exam tip
Code change plus auto restart equals devtools; memorize the exact artifact spring-boot-devtools.
- prototype
- singleton
- request
- session
The short version
Answer B - default Spring bean scope is singleton.
Key concepts in this question
- Bean scopes
- Singleton vs prototype
- Default eager singleton behavior
Why B is correct
Unless declared otherwise, Spring creates one shared instance per container; singleton is the documented default.
Why the others are wrong
- A: Prototype creates a new instance per request and must be declared explicitly.
- C: Request scope is web-only and must be declared.
- D: Session scope is web-only and must be declared.
2V0-7222 exam tip
No scope listed means singleton; prototype, request, session are always explicit.
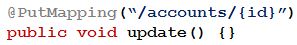
- Add @PathVariable(“id”) String accountId argument to the update() handler method.
- Add @PathVariable long accountId argument to the update() handler method.
- Add @RequestParam long accountId argument to the update() handler method.
- Add @RequestParam(“id”) String accountId argument to the update() handler method.
The short version
A — Explicit @PathVariable name binds the URI id to accountId. The URI template uses id but the method parameter is named accountId, so the name must be declared explicitly.
Key concepts in this question
- @PathVariable: binds a URI template variable to a handler method argument
- Explicit name:
@PathVariable("id")maps{id}to a differently named parameter - @RequestParam: binds a query parameter or form value, not a path segment
Why A is correct
Option A declares @PathVariable("id") String accountId, which correctly maps the {id} path segment to the accountId argument. The explicit value bridges the name mismatch between the URI and the parameter, and String matches an id path variable without risky type conversion.
Why the others are wrong
- B. Uses
@PathVariablewithout an explicit name and alongtype, so it would look for{accountId}rather than{id}and adds an unnecessary conversion. - C. Uses
@RequestParam, which reads query parameters, not path variables, so it never sees the{id}segment. - D. Uses
@RequestParam("id"), which still reads a query parameter namedid, not the path variable.
2V0-7222 exam tip
Path vs query: path variable = part of the URL path; request param = ?id=.... Name mismatch means you must spell the URI name inside the annotation.
- The URLs can be specified via configuration (using authorizeRequests () and request matchers), with the most specific rule first and the least specific last.
- Spring Security can obtain URLs from Spring MVC controllers, the Spring Security configuration just needs a reference to the controller to be protected.
- The URLs are specified in a special properties file, used by Spring Security.
- The URLs can be specified via configuration (using authorizeRequests () and request matchers), with the least specific rule first and the most specific last.
The short version
A — Order URL rules most specific first, least specific last. Spring Security evaluates matchers in declaration order and stops at the first match.
Key concepts in this question
- authorizeRequests: DSL for declaring URL authorization rules
- Request matchers: patterns such as
antMatchersormvcMatchersthat select URLs - First-match-wins: the first matching rule decides access
Why A is correct
Spring Security checks request matchers in the order they are declared, so a general pattern placed first would swallow specific URLs. Declaring the most specific rule first and the least specific last preserves the intended protection for each URL group.
Why the others are wrong
- B. Security does not auto-discover URLs from MVC controllers by referencing a controller; rules must be declared with matchers.
- C. There is no special properties file mechanism for URL interception; it is Java configuration with matchers.
- D. Least-specific-first is reversed and shadows specific rules, so protected or open endpoints would get the wrong decision.
2V0-7222 exam tip
Remember: specific on top, catch-all like anyRequest() at the bottom. If answers swap the order, they are wrong.
- To provide risk governance.
- To drive authentication.
- To manage application users.
- To provide a logout capability.
- To enforce authorization (access control).
- To encrypt data.
The short version
BDE — Security filters authenticate, authorize, and handle logout. Those three are the core runtime jobs of the filter chain.
Key concepts in this question
- Authentication: verifying who the user is
- Authorization: enforcing access control on requests
- Logout: invalidating the session and clearing security context
Why BDE is correct
The Spring Security filter chain drives authentication by processing credentials, enforces authorization by checking authorities against protected resources, and provides logout handling that clears context and session. Together these cover identity, access control, and session termination.
Why the others are wrong
- A. Risk governance is a management process, not a function performed by servlet filters.
- C. Managing application users such as creating accounts is done by user services and repositories, not by security filters.
- F. Encrypting data is done by crypto codecs or TLS, not by authentication and authorization filters.
2V0-7222 exam tip
Think AAA minus accounting: Authentication, Authorization, and Logout. Governance, user CRUD, and encryption are distractors.
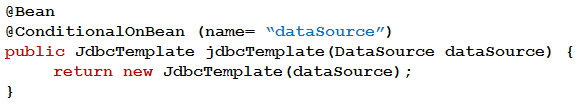
- @ConditionalOnBean(name= “dataSource”) should be replaced with @ConditionalOnBean (DataSource.class) for greater flexibility.
- @ConditionalOnBean(name= “dataSource”) should be replaced with @ConditionalOnMissingBean (DataSource.class) for greater flexibility.
- The @Bean annotation should be removed.
- A JdbcTemplate bean will be created when the DataSource class is in the classpath but there is no DataSource bean.
- A JdbcTemplate bean will be created when a bean named dataSource has already been created.
The short version
Answers A and E - @ConditionalOnBean on dataSource gates JdbcTemplate creation.
Key concepts in this question
- @ConditionalOnBean by name vs by type
- Boot auto-configuration ordering
- JdbcTemplate requires a DataSource bean
Why AE is correct
A advises type-based matching for flexibility, and E correctly states the semantics: JdbcTemplate bean is created only when a bean named dataSource already exists.
Why the others are wrong
- B: @ConditionalOnMissingBean inverts the logic and would create JdbcTemplate when DataSource is absent, which is wrong.
- C: Removing @Bean would remove the bean definition entirely.
- D: The condition requires an existing DataSource bean, not merely the class on the classpath; that describes @ConditionalOnClass.
2V0-7222 exam tip
OnBean means bean must exist; OnMissingBean means it must not; OnClass means class on classpath.
- A setting for specifying which code you want Spring Boot to generate for you.
- A specific POM which you must build to control Spring Boot’s opinionated runtime.
- A pre-existing model project you can download and use as the basis of your project.
- An easy way to include multiple, coordinated dependencies related to a specific technology, like web or JDBC.
The short version
Answer D - starters bundle coordinated dependencies for a technology.
Key concepts in this question
- Spring Boot starters
- Opinionated dependency management
- web, jdbc, test starters
Why D is correct
A starter is a convenience POM that pulls in a tested set of libraries for web, JDBC, validation and similar stacks.
Why the others are wrong
- A: Starters do not generate code; Initializr generates code.
- B: Starters are consumed directly, not something you must build, and they cover compile plus runtime.
- C: Starters are not template projects; they are dependencies.
2V0-7222 exam tip
Starter equals curated dependency bundle; Initializr equals project generator.
- Add @EnableTransactionManagement to a Java configuration class.
- Annotate a class, an interface, or individual methods requiring a transaction with the @Transactional annotation.
- A class must be annotated with @Service and @Transaction.
- A class requiring a transaction must implement the TransactionInterceptor interface.
- Write a Spring AOP advice to implement transactional behavior.
The short version
AB — Enable transactions, then mark them with @Transactional. One switch turns on the machinery, the other declares where it applies.
Key concepts in this question
- @EnableTransactionManagement: activates annotation-driven transaction infrastructure
- @Transactional: declares a class, interface, or method as transactional
- PlatformTransactionManager: the bean that actually manages the transactions
Why AB is correct
Without @EnableTransactionManagement the @Transactional annotations are never processed, and without @Transactional there is no declaration of which methods need transactions. The two together give you infrastructure plus demarcation, which is the documented minimal setup.
Why the others are wrong
- C. There is no
@Serviceplus@Transactioncombination that enables transactions; the annotation is@Transactionalalone. - D. Application classes never implement
TransactionInterceptor; that is framework infrastructure. - E. You do not hand-write AOP advice for standard transactions; the framework provides the advice once enabled.
2V0-7222 exam tip
Two-item checklist: Enable plus Transactional. If an option invents a new annotation or interface, eliminate it.
Want the full bank of 77 questions for VMware Spring Professional (2V0-72.22)? See all practice exams.